Recent Post
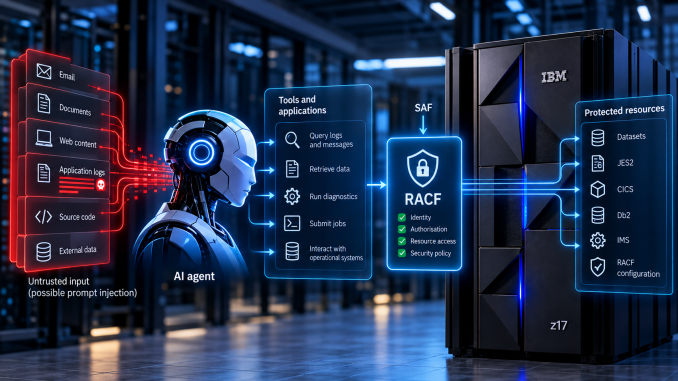
When AI Meets RACF: Can an Authorised Identity Become a Security Risk?
For decades, mainframe security has relied on a fundamental principle: before a user or application is allowed to access a protected resource, the system must determine whether the appropriate authority exists. On z/OS, the System Authorization Facility (SAF) provides a common interface through which resource managers can request security services. RACF, ACF2 and Top Secret are external security managers (ESM) that can enforce the relevant security policies. This is something mainframe security professionals understand very well. But the increasing use of Artificial Intelligence, particularly AI agents capable of interacting with external tools and applications, introduces an interesting security challenge. What [...]